The practice keeps clinical authority
Your licensed team defines the care model, approves clinical policy, receives escalations, and makes final patient-care decisions.
Security, authority, and data boundaries
Kept Count makes work, exceptions, ownership, and review history visible. Your organization keeps clinical judgment, compliance oversight, coding decisions, and final claims authority.
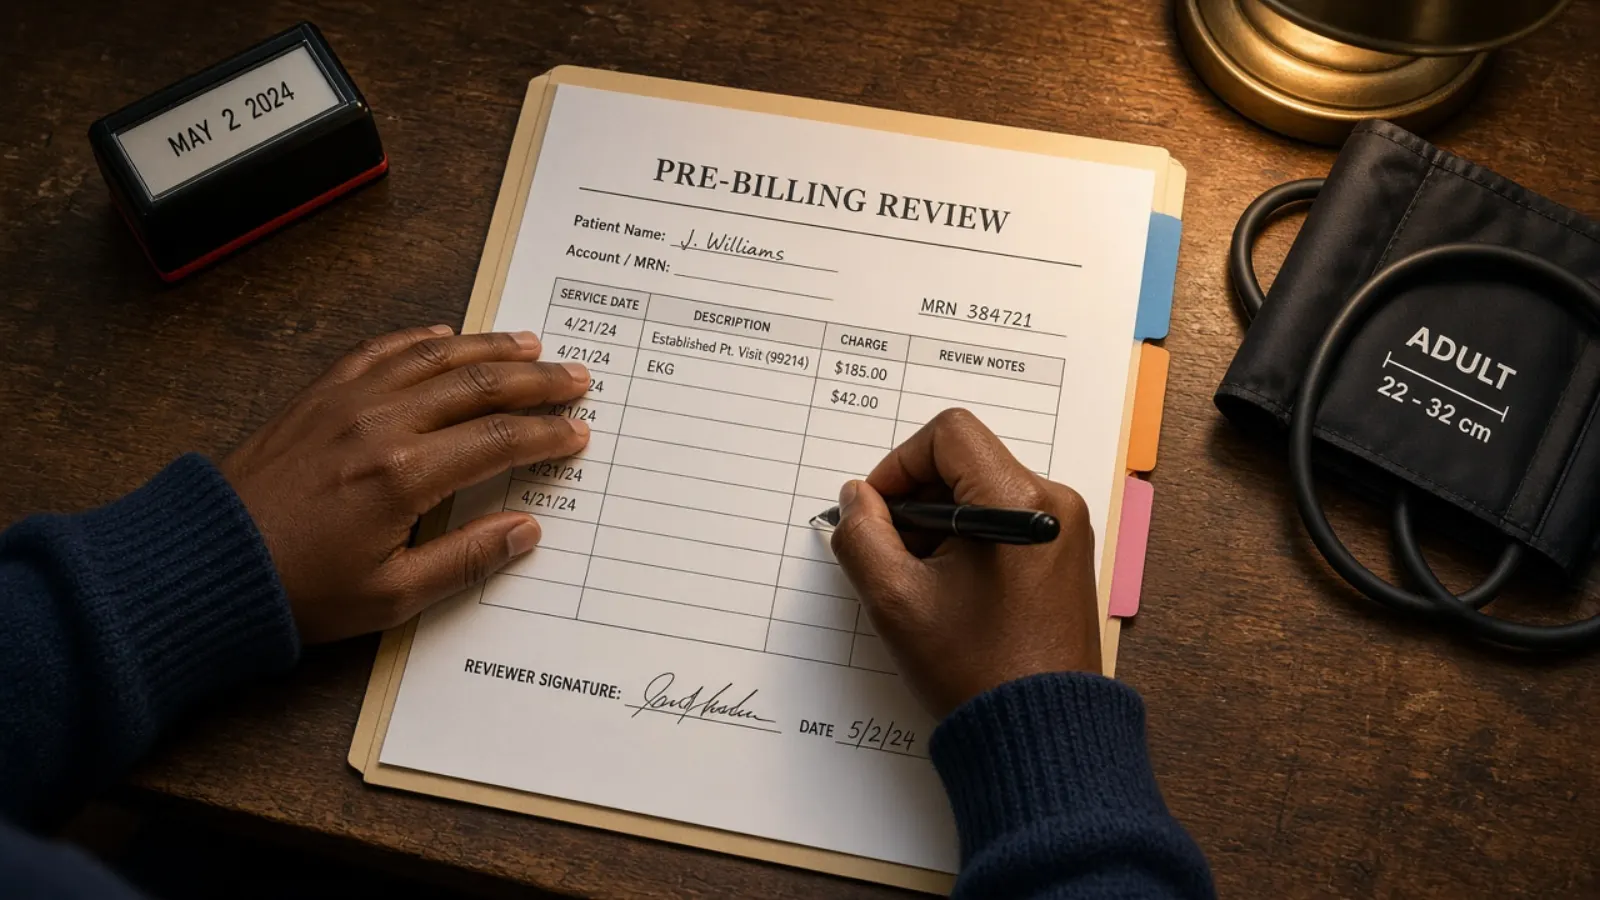
Why the boundary matters
That is the reason authority stays with the people who are accountable for it, at every handoff below.
The control model
Your licensed team defines the care model, approves clinical policy, receives escalations, and makes final patient-care decisions.
Kept Count prepares review-ready evidence. It does not choose final codes, submit claims, receive collections, or release unsupported lines.
Missing consent, conflicting facts, unresolved requirements, and held billing lines remain visible with an owner and reason.
Provisioned users work within assigned roles and organizational boundaries; audit evidence records important actions and changes.
Recount prepares the next contact and can draft attributable notes from the record the worker can already see. It does not approve clinical decisions, release billing lines, send messages, rank the worklist, or replace the named human owner. Covered use requires the appropriate agreements and a dedicated environment; public evaluation stays synthetic.
Provider teams retain patient-level authority while community, sponsor, and network views are limited to approved aggregate or assigned operational information.
CMS and OIG audit-response readiness
Assign owners, preserve a dated decision trail, surface missing or contradictory evidence, and track holds and corrections so your compliance team can monitor the process and prepare for record requests. Kept Count supports this workflow; it does not replace the practice's compliance program or audit plan.
Kept Count can
Organize candidate evidence, monthly work, consent records, exceptions, supervision, QA, and billing-support packets.
A responsible practice reviewer must
Confirm program fit, patient facts, clinical appropriateness, coding, coverage, and the final decision to submit or withhold a claim.
Kept Count does not
Guarantee reimbursement, certify compliance, replace counsel or a compliance officer, auto-submit claims, or make clinical decisions.
Primary requirements and guidance
Data boundary
The public tour and evaluation experience use synthetic or de-identified examples. Real patient information must not enter the system until the contract, BAA, covered-vendor, security, and practice-acceptance gates are complete.
No PHI in public forms
Readiness and walkthrough requests are for business contact and implementation information only.
Production is a gated decision
The practice and Kept Count clear technical, contractual, security, clinical, and billing gates before activation.
Assurance status
A vendor BAA or SOC 2 report does not make its customer HIPAA compliant or transfer a SOC 2 attestation. Kept Count is building a covered production boundary and an independent assurance program; the current public environment remains synthetic-only.
Covered vendor layer
Supabase and Vercel offer HIPAA-capable services under specific paid plans, signed BAAs, and configuration requirements. Kept Count must activate and evidence the exact covered accounts and projects before PHI use.
Kept Count layer
Risk analysis, policies, training, access reviews, incident and recovery procedures, vendor management, and customer activation controls remain Kept Count responsibilities. HHS does not recognize a shortcut “HIPAA certification.”
Independent assurance
Kept Count does not currently hold its own SOC 2 report. The path is an independent HIPAA assessment and penetration test, followed by a scoped SOC 2 examination performed by an independent CPA firm when the controls and evidence period are ready.
Before production activation
These are procurement and implementation controls, not badges. Evidence is reviewed with the responsible owners before the practice authorizes real-data use.
We will walk through the control boundary, the evidence path, and the exact decisions your practice would retain.
Ask Kept Count
Answers from the public site. Nothing here is clinical, coding, or legal advice.
Ask about the product, the monthly workflow, supported programs, security posture, integrations, or the workflow session.